Showing posts with label Dept. of Homeland Security. Show all posts

Thursday, March 1, 2012

Ship Cargo Containers – Finding Out What’s In Them Before There’s Trouble

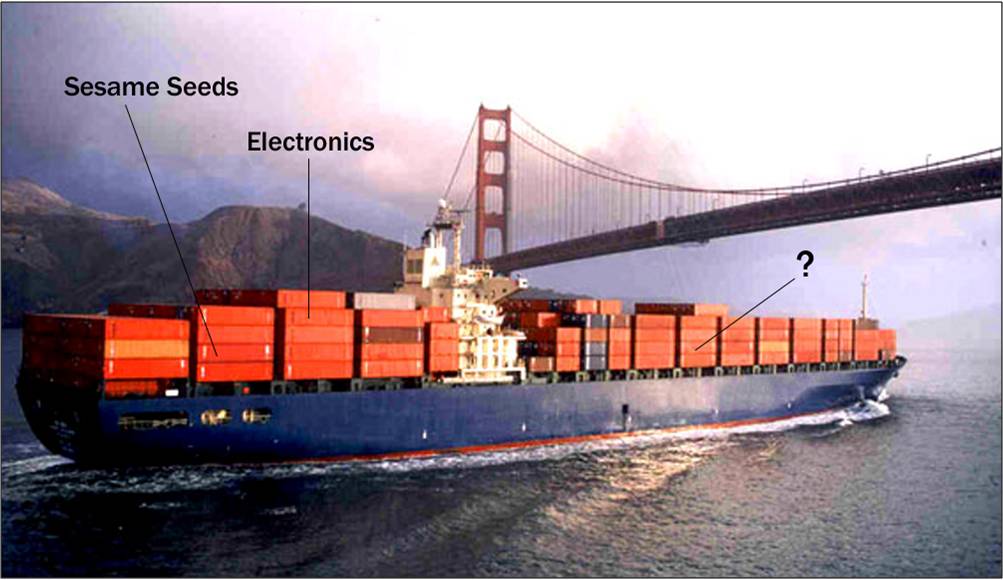
Every day, thousands of cargo containers from around the world pass through our nation’s sea ports carrying items we need, and possibly some that are not so welcome: drugs, explosives, chemical, biological, or radiological weapons – even human cargo. The possible concealment of such items in containers led lawmakers to call for the screening of all ocean cargo containers—thousands per port per day.

The Department of Homeland Security’s (DHS) U.S. Customs and Border Protection (CBP) is charged with the critical task of securing the country from terrorists and their weapons while facilitating legitimate trade and travel, including the monitoring of what’s in thousands of sea cargo containers as they pass through CBP screening. These containers must be inspected quickly and accurately, and without the business at each port grinding to a halt when they do so.

The DHS Science and Technology Directorate (S&T) and its Transportation Security Laboratory (TSL) in Atlantic City, NJ, have developed a way to test technical solutions to this need: the Container Security Test Bed (CSTB) – an outdoor “laboratory” allowing researchers and developers from government, academia, and industry to explore novel ways to detect threats in a cargo container.

The CSTB is run by TSL engineers and simulates exactly the cantilever cranes used to unload container ships. The CSTB allows a container to be picked up, moved, and put down in minutes, mimicking both the way and the timeframe in which each container is taken off a ship and put onto the dock.

“Give me the right tools – a gas chromatograph, a mass spectrometer, and an hour’s time – and I can tell you what’s in a 40-foot container,” said Dave Masters, the S&T Program Manager who oversaw the creation of the Test Bed. “But a maritime container terminal can’t spare an hour. It needs its cranes to move goods, not run experiments. The CSTB gives any new sensor system a real-world workout that replicates both screening the items in a shipping container, as well as the standard loading/unloading operations at a seaport. Sensors must survive the container being hoisted up, moved quickly, and slammed down – they cannot be so delicate that they cannot survive gritty port conditions.”

S&T researchers are encouraging technology developers to test any kind of sensor at the CSTB. Detection technologies constantly undergo improvements in order to detect trace amounts of substances ­­— and do so very quickly. Chemical-based sensors, currently in use for aviation security, may find trace amounts of explosives, drugs, or other illicit substances, while laser-based methods that can “read” the physical properties of target molecules detection methods are also in development.

What is the specific challenge? S&T researchers are collaborating on techniques to get a representative sample of the air inside the container to the sensor itself. Representative samples of air inside a cargo container must be captured through an air vent standard containers have, and then that sample will pass through several variations of detection sensors. This technology was demonstrated to S&T by a joint effort between MIT and Lincoln Labs in 2010.

Alternatively, sensors may be built into the cargo container and programmed to send information on any illicit content to the receiving seaport while the container is still en route. In October 2011, ConSearch, LLC conducted a feasibility demonstration of their in-situ chemical and radiological detection capability. The demonstration consisted of simulating a trans-oceanic voyage of a 40-foot container that contained several threat types and employed a method of using multiple sensors to obtain a comprehensive view of the chemical/radiological content.

To evaluate explosive detection methods, TSL scientists are also are testing methods to present samples to sensors more quickly and accurately.

“We’re exploring the art of the possible. The things we’re doing, you can’t do on paper. You need to get your hands dirty,” says Masters.

The S&T Container Security Test Bed provides a unique opportunity for public and private sector partners to research and collaborate on novel ways to detect threats in a cargo containers—working together to make our shipping industry more safe, secure and resilient.

Monday, November 21, 2011

Making Domain Names Safe and Reliable

Domain Name System Security Extensions (DNSSEC)

As we discussed throughout National Cyber Security Awareness Month, Internet safety is a shared responsibility and each of us has a role to play. The DHS Science and Technology Directorate (S&T) is doing its part to make websites more secure and reliable by enhancing the Domain Name System (DNS), which translates website names like science.com into a network address like 1.2.3.4. Recognizing the Department's role in this effort, the S&T Domain Name System Security Extensions (DNSSEC) project received the National Cybersecurity Innovation Award at the Sans Institute's Second Annual National Cybersecurity Innovation Conference for its innovation in promoting research that "pays off" by focusing on work that can result in real products and real risk reduction.

At the advent of the Internet thirty years ago, the brand new DNS was trusted by everyone. Today, hackers take advantage of our long-standing trust in DNS and work to trick the system by stealing information and redirect-ing our data hundreds, if not thousands, of times every day. S&T and its partners are working to restore trust in the system through the creation and implementation of DNSSEC.

Most websites are not self-contained, but are rather a patchwork of information drawn from scores of sources.  DNSSEC authenticates the existence, ownership, and integrity of data while systematically validating sources including hundreds of servers, or nodes. "The value of DNSSEC reaches far beyond preventing hackers from obtaining login information," said Edward Rhyne, DNSSEC program manager in S&T's Cyber Security Division. "DNSSEC is the foundation for a new trust model for all communications on the Internet, essentially protecting our critical infrastructure."

As governments, banks, Internet service providers, businesses, and other stakeholders increase their awareness of DNS-related threats, DNSSEC adoption is gaining momentum. "Users are starting to understand," said Rhyne. "A hacker may insert a malicious server between a user and their bank, enabling collection of login credentials and account information— essentially allowing the hacker to steal an identity and transfer money as the authorized user."

Since 2004, S&T and its partners, including the National Institute of Standards and Technology and the DNS-SEC Deployment Initiative, have worked to build support for DNSSEC, which has resulted in registrars from all over the world. More than 20 country codes, including .us and .uk, are involved in this effort. In addition, DNSSEC was deployed in the .edu, .gov,.org, .net, and .com zones while top-level domains of the U.S. military's .mil are slated to be DNSSEC-signed in December 2011. Adoption by these most commonly utilized domains paves the way for others, and will ultimately create a complete end-to-end chain. By authenticating and protecting data, DHS is continuously working to build a safer, more secure, and more resilient cyberspace.

Saturday, October 22, 2011

Cyber Commander Presses for Math, Science Education

By Donna Miles
American Forces Press Service

BALTIMORE – Ask the top U.S. cyber warrior how to ensure the next generation of Americans is able to confront future security challenges and he’ll tell you: beef up their math, science and technology education today.

Army Gen. Keith B. Alexander, commander of U.S. Cyber Command and director of the National Security Agency, is on a campaign to boost science, technology, engineering and mathematics education nationwide.

The United States lags behind much of the world in building these capabilities that will be essential to the future national security framework, he told participants today at the International Systems Security Association conference here.

Alexander rattled off statistics about the percentage of graduates around the world earning so-called “STEM” degrees. In China, it’s 47 percent; in South Korea, 38 percent; and n Germany, 28 percent.

In the United States, only 4 percent of all graduates earn STEM degrees. “We’ve got to fix that,” Alexander said.

Recognizing that today’s and tomorrow’s graduates will form the background of the future U.S. security workforce, the National Security Agency is a partner in a nationwide effort to promote STEM education.

In 1998, NSA established centers of excellence to identify universities that provide outstanding information assurance programs. Today, NSA and the Department of Homeland Security co-sponsor the National Centers of Excellence in Information Assurance Education and CAE-Research programs.

The program, which includes 118 colleges and universities, aims to promote higher education and research in these areas, and develop more professionals with information assurance expertise, Alexander explained.

Ultimately, the goal is to reduce vulnerability in the United States’ national information infrastructure.

While calling these and related programs a great step in the right direction, Alexander said they’re not enough. “If we have 4 percent of our graduating classes with STEM, perhaps we could and should be doing better,” he said.

What’s needed, he said, are core science programs beginning as early as elementary school that ultimately will ensure the nation’s long-term security.

“How are we going to educate, not just my grandchildren, but all the other kids their age?” he asked. “How do we get the United States back on the right course for STEM? And what can we do to help push that?”

Friday, October 21, 2011

Science and Technology Directorate Wins Two Awards for Cyber Security

By Doug Maughan, Director, Cyber Security Division, DHS Science & Technology Directorate

Throughout Cybersecurity Awareness Month, we have discussed the importance of making the Internet safer and more secure. This is a shared responsibility, and each of us has a role to play. Emerging cyber threats require the engagement of the entire society—from government and law enforcement to the private sector and most importantly, members of the public. Last week, the Department of Homeland Security’s (DHS) Science and Technology Directorate (S&T) received two awards for work in strengthening our nation’s cybersecurity posture.

We received a National Cybersecurity Innovation Award at the Sans Institute’s Second Annual National Cybersecurity Innovation Conference for our Domain Name System Security Extensions (DNSSEC) project , which protects the public by ensuring that websites visited are the real deal and not imposters. Phony websites steal users’ log-in names, passwords, and even money, from thousands of innocent Internet users every year. S&T’s Cyber Security Division (CSD) was recognized for its innovation in promoting research that “pays off” by focusing on work that can result in real products and real risk reduction. Moreover, the award noted that the CSD’s approach has forced the R&D community to think beyond the theoretical to consider a more practical horizon.

DHS S&T also received the Open Source for America (OSFA)2011 Government Deployment Open Source Award for the Homeland Open Security Technology (HOST) project , which brings together technology leaders from across government and developing advanced open source security solutions that address their prioritized gaps. This award recognize projects and people that educate decision makers in the federal government about the advantages of using free and open-source software and encourage federal agencies to give equal priority to procuring free and open-source software in all of their procurement decisions. The development of the open source intrusion detection system, Suricata, was sponsored through this project and is now being sustainably maintained by industry through a non-profit foundation.

The DHS Science and Technology Directorate is leading efforts to develop and deploy more secure internet protocols that protect consumers and industry internet users. As evidenced by these awards, the Department is making significant strides to enhance the security of the nation’s critical physical infrastructure as well as its cyber infrastructure and networks.

Friday, July 1, 2011

The U.S. And Spain Sign Agreement On Science And Technology Cooperation For Homeland Security Matters

MADRID - Secretary of Homeland Security Janet Napolitano today joined Spanish First Deputy Prime Minister and Interior Minister Alfredo Pérez Rubalcaba to sign an agreement on scientific and technological cooperation - sharing best practices to prevent and detect threats in addition to strengthening research and development.

"International collaboration in science and technology is a major part of our ongoing efforts to counter threats of terrorism," said Secretary Napolitano. "This agreement demonstrates concrete and practical steps that the United States and Spain are taking to further strengthen cooperation and to research while sharing cutting-edge technologies to ensure our mutual security."

During today’s meeting, Secretary Napolitano and Minister Rubalcaba reiterated their commitment to foster bilateral cooperation in scientific and technological fields that have a direct impact on national security—underscoring the need to amplify research, evaluation, and preparation of chemical, biological, radiological, nuclear and anti-explosive protection measures to better protect the flow of commerce and the citizens of both nations.

The agreement, which highlights collaboration with the private sector, public organizations and academic institutions, will support scientific and technological solutions through the following actions:

•Joint and coordinated research to fill technical capability gaps in homeland security needs
•Development of technologies that help prevent and respond to national security threats
•Increased access to national laboratories and universities to carry out research, development, testing, and evaluation activities for homeland security
•Promotion and development of transportation security
•Protection of critical infrastructure
•Establishment of working groups, scientific seminars, and conferences to analyze emerging challenges to national security
•Exchange of technology, staff and information

To date, the United States has signed similar agreements with 11 other nations, such as Australia, Canada, France, Germany, Israel, New Zealand, and the United Kingdom.

Tuesday, June 28, 2011

DHS's First Patent: A Citizen's Dosimeter!

It fits in your wallet and can save your life.

No matter how many plastic cards currently crowd your wallet, one day you may wish to make room for one more. The Department of Homeland Security(DHS)’s Science and Technology Directorate (S&T) has developed a miniaturized version of a dosimeter, a portable device used for measuring exposure to ionizing radiation, which can provide life-saving early detection in the unlikely event of a nuclear accident or dirty bomb.

Dubbed the Citizen’s Dosimeter, this high-tech plastic card would be as convenient and affordable as a subway card, with the capability to measure the amount of radiation on a person or in a given area. The National Urban Security Technologies Laboratory (or NUSTL, pronounced new STEEL) located in New York City and managed by DHS S&T, has been awarded a patent that covers the development of radiation dosimetry technologies – DHS’s first patent.

Currently, personal radiation dosimeter badges are worn in nuclear plants, but a plant dosimeter cannot be read on the spot; it must be sent to a processing lab to determine an individual’s radiation dose. While a final prototype has not yet been built, a workable blueprint for a wallet-sized card that can detect radiation in real time is now in place.

“We were inspired by the Metro cards we use every day to get around Manhattan, and envisioned a dosimeter with that level of convenience,” says Gladys Klemic, a NUSTL physicist who managed the project from Illinois. Klemic believes a dosimeter in this form could benefit both emergency responders and the general public.

Klemic and her team at NUSTL set out to create a dosimeter that would meet American National Standards Institute (ANSI) requirements for personal radiation dosimeter badges, and incorporate commercially available components to decrease the size and lower the price tag.

NUSTL began by using radiation-sensitive material from Landauer, Inc., a commercial dosimetry provider in Illinois, testing materials of varying thicknesses and combinations to determine how thin they could make the card while still achieving the targeted performance. After testing nearly a half a dozen materials, the NUSTL scientists determined that using the chemical element tantalum allowed them to obtain accurate readings with minimal thickness. Combining this element in a unique double-layer, stainless steel filter helped to reduce false positives. It was this unique design that led to the patent award.

The next step is to develop a card reader to reveal the radiation dose measured by the Citizen’s Dosimeter. In the event of a nuclear incident, first responders equipped with a card reader would immediately be able to measure radiation exposure for anyone carrying the Citizen’s Dosimeter. While it will be years before a card and reader can be prototyped, tested, certified and wallet-ready, NUSTL has lined up a team to support the effort, including:

•Engineers at StorCard, a California-based group that has previously developed a prototype credit-card floppy disk and reader
•Nomadics, an Oklahoma engineering firm
•Radiation detection experts at Landauer and Oklahoma State University
The Citizen’s Dosimeter represents a technological breakthrough and the next generation in radiation detection. It also demonstrates how public-private partnerships can work to produce life-saving solutions – in this case, protecting the nation from radiation resulting from an act of terrorism or natural disaster.

Friday, June 17, 2011

Where There’s Smoke, There's a Signal

For firefighters, wireless self-powered router “breadcrumbs” that won’t become toast when baked or soggy when hosed

Cellular phones, Global Positioning System (GPS), WiFi, Bluetooth…the list goes on. In today’s modern world, digital signals connect us to friends, family, colleagues and just about anyone else in countless ways. In fact, it’s hard to imagine maintaining these relationships without the aid of digital communications.

Yet, despite the ubiquity of such devices, with few exceptions, today’s firefighters still rely on 20th century radios, whose outdated analog signals have trouble penetrating debris and concrete. When a firefighter heroically plunges into a smoke-filled building, tunnel, or forest, UHF radio or, for that matter, even a GPS satellite signal won’t follow. The firefighters vanish from the map.

That’s why the Department of Homeland Security’s (DHS) Science and Technology Directorate (S&T) is combining two previously developed heatproof and waterproof wireless monitors, with a newly developed technology that working together could lead to a life-saving solution.

One device, the Geospatial Location Accountability and Navigation System for Emergency Responders (GLANSER), crams a microwave radio, a lightweight battery, and a suite of navigation devices into a tracking device the size of a paperback book. Back at the fire truck, GLANSER’s signals are received and transmitted by a small, USB-powered base station plugged into a laptop. As firefighters move from room to room and floor to floor, the laptop animates their every step.

A second device, the Physiological Health Assessment System for Emergency Responders (PHASER), can monitor a firefighter’s body temperature, blood pressure, and pulse, and relay these vitals back to the base station. If a firefighter falls or faints, fellow firefighters can race in, quickly find him, and bring him to safety – guided by GLANSER.

Like the first cordless phones, GLANSER and PHASER transmit at 900 MHz—a frequency that can penetrate walls, given a decent-sized transmitter. But because of their portable size, the transmitters are extremely modest. Their signals could be stopped by a wall, or—in a wildfire—a wall of trees, unless relayed by routers. That presents an infernal challenge.

What’s needed is a self-powered router that can take the heat.

S&T is developing a tiny, one-inch square, ½-inch thick, throwaway router that’s waterproof and heat-resistant up to 500° F. The Wireless Intelligent Sensor Platform for Emergency Responders, or WISPER, contains a two-way digital radio, antenna, and 3-volt lithium cell.

Here’s how it works: Each firefighter enters a burning building with five routers loaded into a belt-mounted waterproof canister. If a firefighter steps behind concrete or beyond radio range, the base station orders his canister to drop a “breadcrumb.” The dropped routers arrange themselves into a network. If a router accidentally gets kicked down a stairwell or firehosed under a couch, the WISPER network will automatically reconfigure.

To an embattled firefighter, a handful of these smart “breadcrumbs” could be the difference between life and death.

To extract the most life from the router’s tiny battery, WISPER’s designers turned to a simple, low-power communications protocol, ZigBee. ZigBee is tortoise-slow by design: trading speed for battery life, telegraphing no more than 100 kilobits per second (kbps) – more than 99 percent slower than WiFi.

“Throw in smoke, firehose mist, stairwells, and walls, and you’re down to maybe 10 kbps. But that’s fast enough to tell an incident commander the whereabouts (via GLANSER) and health (via PHASER) of every firefighter in the blaze,” explains Jalal Mapar, WISPER’s project manager in S&T’s Infrastructure Protection and Disaster Management Division. “We’re not streaming video that needs a lot of bandwidth, just vital signs and coordinates.”

WISPER’s router, dispenser, and tiny USB base station were developed by Oceanit Laboratories, Inc., of Honolulu, and the University of Virginia’s Department of Computer Science under an S&T Small Business Innovation Research (SBIR) program.

In March 2011, Oceanit and UVA demonstrated WISPER for S&T at a FEMA office in Arlington, Virginia. Simulating a squad of firefighters, three router-bearing researchers fanned out, dodging around corners, stepping down stairwells. In test after test, their signals stayed strong, even at up to 150 feet.

Now that the SBIR project is proven to be a surefire success, S&T hopes a maker will step forward to produce the routers in volume. Once a commercial entity begins production, S&T’s Test & Evaluation and Standards Office will evaluate a sample product to ensure it meets the stated performance criteria and for consistency. They will also set industry standards so that other manufacturers will have set specifications for design and performance.

“We’ve demonstrated that it works,” says Mapar. “Now we just need a private sector partner to add fuel to the fire.”

Wednesday, March 2, 2011

Coming Soon to an App Store Near You: Mobile Technology for Information Collection and Dissemination

DACS will soon publish a report on the "Use of Mobile Technology for Information Collection and Dissemination."

This blog post was shared by the Data & Analysis Center for Software.

Have you ever wondered how the government is embracing the world of mobile technology? If so, you’re in luck.

The Data & Analysis Center for Software (DACS) will soon publish a Critical Review/Technology Assessment Report on the “Use of Mobile Technology for Information Collection and Dissemination.” This report, focused on government organizations considering mobile technology, examines how new mobile technology such as the iPhone, iPad, and Android based devices have completely revolutionized the way information can be both collected and distributed. As a result, numerous organizations like the Department of Defense (DOD), the U.S. Army, and the Department of Homeland Security have already begun leveraging mobile technology as an information medium.

So, why should an organization embrace mobile based technology? Easy – convenience and flexibility. These applications provide soldiers in the field with the ability to access critical operational information regardless of their location. This could include anything from classified intelligence to maps. All of this information can be requested and received virtually instantaneously using mobile technology. Additionally, when used in conjunction with add-on sensors, mobile devices can be used to detect and map such events as chemical and biological attacks.

The DACS report highlights many of the applications already developed and in use by numerous branches of the government, including law enforcement agencies. It also identifies current research and development helpful to those individuals tasked with making crucial infrastructure decisions as they relate to mobile devices. This could include individuals looking to migrate from a traditional computer based infrastructure to a more mobile device based infrastructure or individuals in charge of deploying mobile technology in the field.

The DACS report will soon be available on its website, accessible via DTIC’s Information Analysis Centers website.

The Data and Analysis Center for Software (DACS) is the DOD Center of Excellence responsible for acquiring, archiving, analyzing, synthesizing, and disseminating scientific and technical information related to Software Technology and Software Engineering.

Interested in learning more or working with DACS on an upcoming effort? DACS can be reached via the IAC website or the DACS website.

Tuesday, January 25, 2011

Secret Service Site Security Training Gains a High-Tech Edge

Chemical releases, suicide bombers, air and subsurface threats:  the U.S. Secret Service needs to be prepared to handle these real-life incidents.  Training to respond to such incidents, however, has been more theoretical than practical. Now, with the help from the Department of Homeland Security (DHS) Science & Technology Directorate (S&T), the Secret Service is giving training scenarios a high-tech edge:  moving from static tabletop models to virtual kiosks with gaming technology and 3D modeling.

For the past 40 years, a miniature model environment called “Tiny Town” has been one of the methods used to teach Secret Service agents and officers how to prepare a site security plan. The model includes different sites -- an airport, outdoor stadium, urban rally site and a hotel interior -- and uses scaled models of buildings, cars and security assets. The scenario-based training allows students to illustrate a dignitary’s entire itinerary and accommodate unrelated, concurrent activities in a public venue.  Various elements of a visit are covered, such as an arrival, rope line or public remarks.  The class works as a whole and in small groups to develop and present their security plan.

Enter videogame technology.  The Secret Service’s James J. Rowley Training Center near Washington, D.C., sought to take these scenarios beyond a static environment to encompass the dynamic threat spectrum that exists today, while taking full advantage of the latest computer software technology.  The agency’s Security and Incident Modeling Lab wanted to update Tiny Town and create a more relevant and flexible training tool.

With funding from DHS S&T, the Secret Service developed the Site Security Planning Tool (SSPT), a new training system dubbed “Virtual Tiny Town” by instructors, with high-tech features:

•3D models and game-based virtual environments
•Simulated chemical plume dispersion for making and assessing decisions
•A touch interface to foster collaborative, interactive involvement by student teams
•A means to devise, configure, and test a security plan that is simple, engaging, and flexible
•Both third- and first-person viewing perspectives for overhead site evaluation and for a virtual “walk-through” of the site, reflecting how it would be performed in the field.
The new technology consists of three kiosks, each composed of a 55” Perceptive Pixel touch screen with an attached projector and camera, and a computer running Virtual Battle Space (VBS2) as the base simulation game. The kiosks can accommodate a team of up to four students, and each kiosk’s synthetic environment, along with the team’s crafted site security plan, can be displayed on a large wall-mounted LED 3D TV monitor for conducting class briefings and demonstrating simulated security challenges.

In addition to training new recruits, SSPT can also provide in-service protective details with advanced training on a range of scenarios, including preparation against chemical, biological or radiological attacks, armed assaults, suicide bombers and other threats.

Future enhancements to SSPT will include modeling the resulting health effects and crowd behaviors of a chemical, radiological or biological attack, to better prepare personnel for a more comprehensive array of scenarios and the necessary life-saving actions required to protect dignitaries and the public alike.

The Site Security Planning Tool development is expected to be completed and activated by spring 2011.

Monday, September 27, 2010

DHS Works with Partners Across the Country and Around the World to Assess the Nation's Cyber Incident Response Capabilities

Department of Homeland Security (DHS) Secretary Janet Napolitano today announced the beginning of Cyber Storm III—a three-day long, DHS-sponsored exercise that brings together a diverse cross-section of the nation’s cyber incident responders to assess U.S. cyber response capabilities.

“Securing America's cyber infrastructure requires close coordination with our federal, state, international and private sector partners,” said Secretary Napolitano. “Exercises like Cyber Storm III allow us build upon the significant progress we’ve made in responding to evolving cyber threats.”

Cyber Storm III is an exercise scenario that simulates a large-scale cyber attack on critical infrastructure across the nation. The goal of the exercise is to examine and strengthen collective cyber preparedness and response capabilities, involving thousands of participants across government and industry.

As part of Cyber Storm III, DHS will exercise elements of the newly-developed National Cyber Incident Response Plan (NCIRP)—a blueprint for the Nation’s cybersecurity incident response.

Cyber Storm III participants include:

•Administration-Wide—Seven Cabinet-level departments including Commerce, Defense, Energy, Homeland Security, Justice, Transportation and Treasury, in addition to the White House and representatives from the intelligence and law enforcement communities.
•Eleven States—California, Delaware, Illinois, Iowa, Michigan, Minnesota, North Carolina, New York, Pennsylvania, Texas, Washington, as well as the Multi-State Information Sharing and Analysis Center (ISAC).
•12 International Partners—Australia, Canada, France, Germany, Hungary, Italy, Japan, the Netherlands, New Zealand, Sweden, Switzerland, and the United Kingdom.
•60 Private Sector Companies—DHS worked with representatives from the Banking and Finance, Chemical, Communications, Dams, Defense Industrial Base, Information Technology, Nuclear, Transportation, and Water Sectors, as well as the corresponding Sector Coordinating Councils and ISACs, to identify private sector participants.

Cyber Storm III also represents the first major exercise testing the new National Cybersecurity and Communications Integration Center (NCCIC)—which serves as the hub of national cybersecurity coordination and was established in October of 2009.

For more information on Cyber Storm III, please visit: www.dhs.gov/files/training/gc_1204738275985.shtm.

For more information on the progress DHS has made in strengthening cyber preparedness and response capabilities, please visit: www.dhs.gov/xlibrary/assets/defending-against-cyber-attacks-september-2010.pdf (PDF, 4 pages - 35 KB).

Sunday, August 30, 2009

Doing Your Part For National Cyber Security Month

October is National Cyber Security Awareness Month.

"Protect Yourself Before You Connect Yourself".


National Cyber Security Alliance Launches
Cyber Security Awareness Volunteer Education (C-SAVE) Program Focuses on bringing Cybersecurity Experts Into Nation’s K‐12 Schools To Educate Students and Teachers about Internet Safety and Security

SAN FRANCISCO, April 22, 2009 – With studies finding that less than 25%** of educators feel comfortable teaching students how to keep themselves safe from online cyber predators, bullies, and online fraud, the National Cyber Security Alliance (NCSA) has focused much of its efforts on providing K‐12 schools with the resources they need to better equip today’s digital generation.

Today at the RSA Conference, the NCSA announced the launch of a nationwide initiative – the Cyber Security Awareness Volunteer Education Program (C‐SAVE) – that is focused on fostering opportunities for cybersecurity experts and IT security professionals to donate their time and tap their expertise to help educate elementary, middle, and high school students about Internet security and safety.

“There is an Internet safety and security knowledge gap,” said Michael Kaiser, executive director of the NCSA. “As we evolve into web based culture, our schools have not kept pace in teaching our youth to develop the skills they need to stay safe and secure online. Only 18%** of K‐12 curriculum discusses identity theft and only 22%** of teachers are comfortable teaching about cyberbullying. In these difficult financial times, C‐SAVE provides schools with a cost‐free opportunity to enrich the education experience and help improve the everyday lives of both their students and their teachers. It also provides information security professionals a wonderful opportunity to give back to their community.”

NCSA is seeking motivated individuals and corporations to approach local schools to deliver the C‐SAVE program. A comprehensive set of learning materials designed by a U.S. Department of Education veteran is available at www.StaySafeOnline.org/CSAVE.

Suggested lesson plans designed to meet the developmental level of young people at all grade levels provide clear, easy to understand instructions and tips for working in a classroom setting. In addition, resources are available that allow teachers and administrators to continue the conversation with their students and their students’ parents.

“We are living in a time when many of our children know much more about how to use the technology than their teachers and parents,” said Bill Sanderson, principal of the International Studies Academy high school in San Francisco. “Most of our students spend more time on the computer each day then they do watching television. School and parents have a responsibility to ensure that students can use computers safely, C‐SAVE will help better educate our children by leveraging the expertise of those who bring significant life experience making computers more secure. In turn, this program will also allow our teachers to better understand the online challenges our students face and better prepare them to harness the power of the Internet safely and securely.”

C‐SAVE also provides the opportunity to introduce students to the possibility of cybersecurity as a profession and become part of the next generation of cyber defenders. As part of the lesson plans, cybersecurity professionals are encouraged to talk about their job and the path they took to get to where they are.

EMC Corporation is the world’s leading developer and provider of information infrastructure technology and solutions that enable organizations of all sizes to transform the way they compete and create value from their information. Striving to be active and socially responsible in its local and global communities, EMC encouraged its cybersecurity experts to participate in C‐SAVE. More than 25 EMC security practitioners have already agreed to volunteer at schools from Massachusetts to California and help train more than 1000 families on staying safe online.

“There is no doubt that both our nation’s students and teachers need assistance when it comes to Internet safety and security,” said Roland Cloutier, Vice President and Chief Security Officer of EMC Corporation. “Companies such as EMC and others have a vast amount of resources that can not only help to keep our children safer online, but also foster a better understanding of the responsibilities one must embrace when using the Internet.”

C‐SAVE was launched in collaboration with the NCSA’s K‐12 education working group and its corporate sponsors.

** Data from 2008 K‐12 National Cyberethics, Cybersafety, Cybersecurity Baseline Study. Full results can be found at wwwStaySafeOnline.MediaRoom.com/

About NCSA

The National Cyber Security Alliance is a nonprofit organization. Through collaboration with the government, corporate, non‐profit and academic sectors, the mission of the NCSA is to empower a digital citizenry to use the Internet securely and safely protecting themselves and the cyber infrastructure. NCSA works to create a culture of cyber security and safety through education and awareness activities. Visit www.StaySafeOnline.org for more information.

Contacts:

Aimee Larsen-Kirkpatrick
National Cyber Security Alliance
Phone: 202-756-3616
email: aimee@staysafeonline.org

Joshua Zecher
463 Communications
202-463-0013, ext. 206
email: josh.zecher@463.com


About National Cyber Security Awareness Month

National Cyber Security Awareness month now in its sixth year is a coordinated effort of the National Cyber Security Alliance, The Department of Homeland Security (DHS), and The Multi-State Information Sharing and Analysis Center (MSISAC).

Source: National Cyber Security Alliance